
Co-Working
Handle multi-tenant cabling, ISP handoffs, and riser coordination by confirming building rules before ordering service, documenting the demarc-to-suite pathway, securing landlord access approvals, and assigning one accountable coordinator. Start 60-90 days before occupancy when possible because riser access and carrier construction can control the move-in date.
What should I confirm before ordering internet for a multi-tenant office?
“John brought the right knowledge to my issue and resolved it in about a reasonable amount of time. I walked away confident the problem was actually fixed.”
Start with a building infrastructure discovery, not an ISP order form. Ask property management which carriers serve the property, where each carrier enters the building, who controls access to the main telecom room, and whether a building-wide telecom agreement affects your choices.
Request current drawings or complete a documented walkthrough of the MDF, IDFs, riser closets, suite entry point, conduit routes, available pathway capacity, electrical provisions, and after-hours access rules. In older metro Atlanta properties, carrier availability at the street does not guarantee a clear route into a specific suite.
For a coworking operator, define the service model before selecting bandwidth. Private-office members, enterprise suites, hot-desk users, guest Wi-Fi, VoIP, cameras, door access, conference rooms, and staff operations may share physical connectivity while requiring different network policies.
Create a written responsibility matrix naming the owner or manager, building engineer, leasing contact, ISP project manager, low-voltage contractor, network provider, and tenant representative. State who approves access, pulls cable, supplies equipment, and signs off at every handoff.
- Confirm carrier availability for the specific building and suite.
- Identify the MDF, IDFs, riser closets, and customer-side pathway.
- Obtain building access, contractor, and insurance requirements.
- Assign a named owner for every approval and installation handoff.
Takeaway: A verified building pathway and responsibility matrix protect the schedule better than a carrier availability quote.
How do I plan the ISP handoff from the demarc to my suite?
The ISP handoff begins at the demarcation point, commonly called the demarc. This is where the carrier’s responsibility typically ends and the customer or building-side pathway begins. Do not assume the carrier will extend service from the basement, MDF, or telecom closet to your office without a separately defined scope.
Ask the carrier to identify the exact handoff location, media type, connector, circuit identifier, rack or wall position, power requirement, and testing responsibility. An Ethernet handoff in a shared MDF may require your contractor to install a fiber or copper extension to your suite’s IDF.
Document the pathway segment by segment: demarc to riser, riser to floor closet, floor closet to suite, suite entry to firewall, and firewall to network switching. Photograph labels and access points after installation. Clear records reduce finger-pointing when a circuit tests clean at the demarc but fails to reach the business network.
Key planning figure: Begin carrier, riser, and pathway coordination 60-90 days before the planned move-in or service date.
For resilience, decide whether a second connection should use a separate carrier, diverse building entry, different riser route, or cellular failover. Two circuits that share one building entry or one closet can still fail together during damage, power loss, or construction work.
In a shared office environment, terminate the handoff behind a managed firewall and build separate VLANs or equivalent segmentation for member networks, guests, operations, cameras, access control, and building-management devices. A fast circuit without segmentation can expose one member’s devices to another tenant’s activity.
Takeaway: Treat the demarc-to-firewall route as a defined construction and network project, not an assumed extension of the ISP order.
Who coordinates riser access, and what approvals are needed?
The property owner or manager usually controls riser pathways, common-area telecom rooms, roof access, penetrations, and work hours. The tenant controls its suite, while the carrier controls its network service. A successful project connects those responsibilities through documented approvals rather than informal promises.
Before work begins, submit the building’s required certificate of insurance, contractor information, scope of work, pathway drawings, proposed cable type, firestopping approach, and requested access dates. Confirm whether the property requires union labor, an approved vendor list, security escort, permit, or engineering review.
Riser work must preserve fire-rated barriers. Whenever cable penetrates a rated wall or floor assembly, use the building-approved firestop system and record the location. Unsealed penetrations create safety and liability problems and may delay inspection, tenant turnover, or future construction.
Coordinate with other building activity. Elevator reservations, ceiling work, tenant improvements, security restrictions, and loading-dock schedules can affect a cable pull. Across metro Atlanta’s distributed office parks and business corridors, missed onsite coordination can create costly repeat visits.
Use one change log for access approvals, drawings, field discoveries, owner decisions, carrier milestones, and completion photos. This creates the accountability trail needed when a proposed route differs from the original plan.
Takeaway: Riser access is a property-governance issue as much as a cabling issue.
What cabling design supports reliable coworking and flexible office operations?
Design structured cabling around business use, growth, and serviceability. Each private office, conference room, access point, camera, printer area, reception desk, and access-control door should have a labeled cable run, documented termination point, and known switch port. Avoid undocumented patching that turns a simple move into a troubleshooting event.
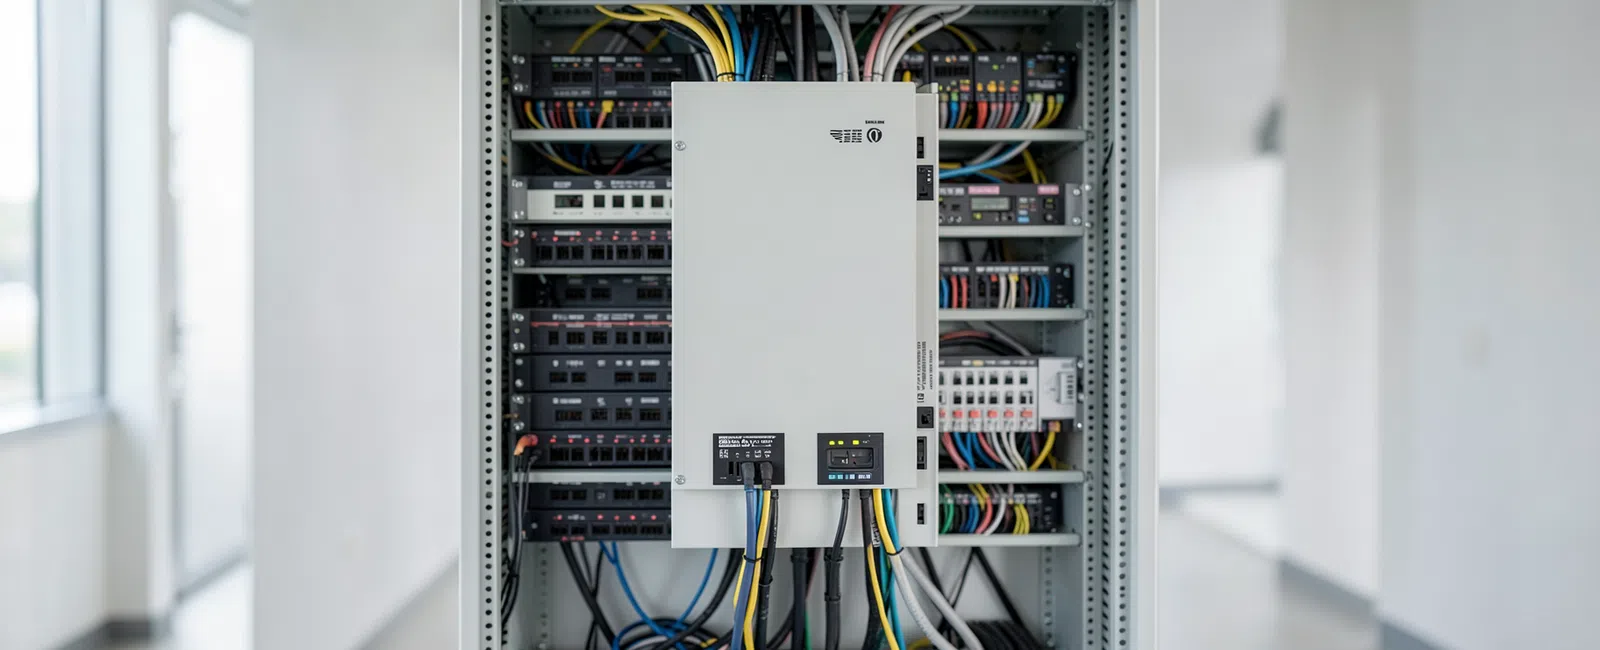
Use a central MDF or suite-level IDF with properly sized rack space, ventilation, power, grounding, cable management, and room access controls. Keep network electronics out of public closets and avoid using extension cords or shared convenience outlets as permanent infrastructure.
Plan horizontal cabling with spare capacity. A coworking space regularly changes room layouts, adds members, introduces new devices, and rearranges shared areas. Extra pathways and reserved rack capacity are less disruptive than reopening finished walls when the next enterprise suite needs additional drops.
Wireless design depends on the wired foundation. Access-point placement, PoE capacity, switch uplinks, cable certification, wall materials, and RF conditions all affect user experience. The Wi-Fi 6 versus Wi-Fi 7 for commercial buildings guide explains why a wireless upgrade should be evaluated as part of a broader infrastructure decision.
For shared spaces, align cabling with the security plan. Cameras, door controllers, visitor systems, and network equipment should be separated from member traffic and documented for authorized support. GDS Technology can coordinate structured cabling and low-voltage infrastructure with business video surveillance systems so physical and network requirements are considered together.
Takeaway: A labeled, certified, expandable cabling system makes flexible workspace operations easier to scale and safer to support.
How do I test the installation and avoid a failed move-in day?
Do not accept “installed” as the same as “operational.” Run a go-live test that confirms the carrier circuit, firewall, switching, Wi-Fi, VLAN separation, VoIP, printing, cameras, access control, remote access, and monitoring work as intended from the actual suites and common areas.
Test failure conditions too. Disconnect the primary connection if failover is part of the design, confirm alerting reaches the right people, verify support contacts know the escalation path, and ensure equipment labels match current documentation. A recovery process that has never been tested is only an assumption.
Make remaining risks visible before members arrive. If a carrier circuit is temporary, a riser repair is pending, a camera is waiting on final placement, or a conference room has incomplete AV, assign an owner and date rather than allowing the issue to disappear into a contractor email thread.
This operational discipline reflects the readiness gap covered in the Built, Wired & Secured episode Is Your Building Ready for Real Operations?. Technical completion matters, but occupants experience the quality of the final operating environment.
Madhav, a professional services client, said, “John brought the right knowledge to my issue and resolved it in about a reasonable amount of time. I walked away confident the problem was actually fixed.” That confidence comes from ownership, documentation, and follow-through - not from simply closing a ticket.
For a metro Atlanta coworking operator, a Technology Partner can connect building-side work with tenant onboarding, ongoing managed IT services, and secure operational support. That continuity prevents infrastructure decisions from becoming recurring member-service problems.
Takeaway: Validate the real user experience, document unresolved risk, and establish escalation ownership before calling the site ready.
Frequently Asked Questions
How early should I start ISP and riser coordination for a new office?
Start 60-90 days before the planned occupancy date whenever possible. That window allows time to confirm carrier availability, receive building approvals, coordinate riser access, complete construction, and test service. Complex buildings, new carrier construction, or restrictive access rules can require more lead time.
What is the difference between an ISP demarc and the office network?
The demarc is the point where the ISP delivers its service and its normal responsibility ends. Your office network begins with the customer-side extension, firewall, switches, Wi-Fi, and devices. The pathway between them must be defined, approved, installed, labeled, and tested as part of the project.
Can a coworking space use one internet connection for every member company?
Yes, one connection can serve a coworking space when the network is designed for capacity, security, and supportability. Separate member, guest, staff, printer, camera, and access-control traffic with VLANs or equivalent controls. Consider redundant connectivity or failover where uninterrupted member operations are a requirement.
Who is responsible for cable runs inside a building riser?
Responsibility depends on the lease, building rules, carrier agreement, and approved scope of work. Property management commonly controls riser access, the carrier delivers its service, and the tenant or its contractor funds customer-side extensions. Put every responsibility, approval, and handoff in writing before work begins.


