
CRE
Before acquiring a commercial property or management portfolio, document network infrastructure, carrier and riser rights, cybersecurity exposure, building-system dependencies, vendor contracts, data ownership, and recovery readiness. Complete the review before closing and assign 30-day transition actions, because one undocumented MDF, expired circuit, or exposed camera network can create immediate operational risk.
What technology assets should a buyer inventory before closing?
“John assessed our setup and moved immediately. He knew exactly what needed to be done and handled it quickly and professionally. You get a partner who sees the work before you have to explain it.”
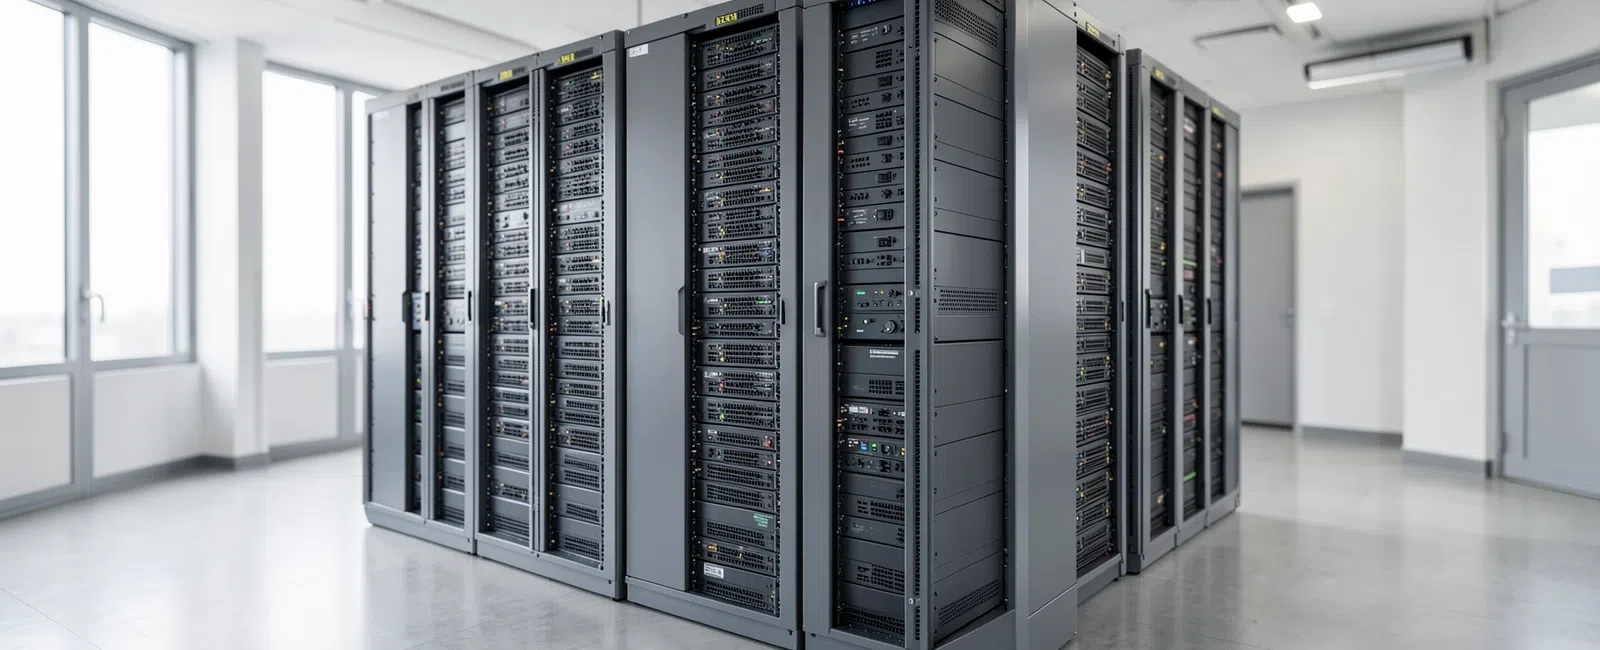
Start with a site-by-site inventory, not a high-level statement that a building has “Wi-Fi” or “security.” Identify every MDF, IDF, demarcation point, switch, firewall, wireless access point, fiber run, UPS, rack, and low-voltage pathway. Record the asset owner, age, serial number, physical condition, support status, configuration backup status, and replacement dependency.
Map technology by business function. Separate systems that support property management, tenant connectivity, common-area Wi-Fi, leasing offices, access control, video surveillance, elevators, life-safety coordination, HVAC or BAS integrations, and vendor-operated equipment. This prevents buyers from treating a shared network as a single utility when it supports several business-critical functions.
- Inventory every telecom room, rack, pathway, circuit handoff, network device, and building-system gateway.
- Identify the legal or operational owner for each asset, account, contract, and configuration backup.
- Record the business function, current support status, physical condition, and replacement dependency.
- Flag undocumented equipment, inaccessible rooms, water damage, unlabeled fiber, and unsupported hardware as transition risks.
Inspect physical pathways as carefully as electronic equipment. A congested riser, unlabeled fiber backbone, inaccessible telecom room, water-damaged enclosure, or undocumented tenant cabling can delay suite turn-ups and make future tenant improvements more expensive. For multi-tenant properties, confirm who controls riser access and who approves carrier work.
Ask for current topology diagrams, port maps, IP-address records, equipment warranties, maintenance histories, and configuration exports. If those records do not exist, document the gap as a transition risk rather than assuming the environment is simple. A buyer needs an accurate baseline before deciding what to retain, replace, or standardize.
GDS Technology’s commercial real estate technology support reflects the practical overlap between connectivity, tenant experience, physical infrastructure, and daily property operations.
Takeaway: An asset inventory must show what exists, who owns it, what it supports, and what fails if it goes offline.
How should buyers assess connectivity, carrier contracts, and riser capacity?
Verify every active internet, voice, fiber, and managed-network agreement directly with the carrier or provider. Capture circuit IDs, service addresses, bandwidth, contract end dates, renewal terms, early-termination obligations, billing contacts, demarcation locations, and escalation procedures. A circuit billed to a former owner or tenant may not transfer automatically at closing.
Review the difference between building connectivity and tenant connectivity. A property may have robust service to the building but inadequate pathways, capacity, or carrier options to individual suites. Confirm available providers, riser capacity, fiber routes, conduit condition, access rules, and the standard process for a tenant move-in, move-out, or urgent outage.
Test critical paths where possible. A current invoice does not prove that failover works, that the documented handoff is correct, or that the carrier can access the right telecom room. Check whether redundant connections terminate through diverse paths and whether power protection supports network equipment during a short outage.
For Norcross and the broader I-85 business corridor, carrier coordination and quick field access affect occupancy because office, flex, light-industrial, and mixed-use sites can have very different connectivity needs within the same market. Identify buildings where a carrier visit, landlord approval, or riser-access restriction could delay tenant service or revenue.
Use the findings to create a portfolio connectivity standard. It can allow different vendors and building types while still setting minimum requirements for documented demarcations, supported firewalls, backup connectivity for critical sites, and named ownership of carrier relationships.
Takeaway: Confirm service rights and physical delivery paths, not merely the name of the internet provider on an invoice.
Which cybersecurity and smart-building risks belong on the checklist?
Review every network boundary and every device class that touches it. This includes firewalls, remote-access tools, cloud administration accounts, Wi-Fi networks, cameras, access-control panels, intercoms, printers, BAS gateways, IoT sensors, and vendor support connections. Determine whether credentials are unique, multifactor authentication is enabled, logging is retained, and administrative access can transfer cleanly.
Network segmentation is a core acquisition question. Tenant traffic, guest Wi-Fi, property-management systems, security devices, and building operations should not share unrestricted access. One compromised tenant-facing device should not provide a route to video footage, door controls, accounting data, or connected building systems.
Assess patching and supportability. Identify unsupported operating systems, end-of-life switches, unmanaged network equipment, default passwords, unknown cloud tenants, and security appliances without active subscriptions. Document what remediation requires an outage, a vendor visit, or a replacement project so the buyer can budget and schedule it responsibly.
Georgia buyers should also evaluate incident readiness. A portfolio may hold tenant, employee, visitor, camera, access-control, or leasing information that could create breach-response duties if exposed. Confirm who can identify affected systems, preserve evidence, contact vendors, and restore operations after an incident.
Cybersecurity diligence should also examine whether security footage and access events are protected from tampering or unauthorized disclosure. Review retention settings, user roles, remote-viewing permissions, storage location, and the ability to export evidence when a property incident requires it. See how these systems fit within a broader commercial property cybersecurity approach.
Takeaway: Treat cameras, doors, Wi-Fi, and building devices as operational technology that needs the same ownership and security discipline as business IT.
What operational, vendor, and continuity evidence should the buyer request?
Request contracts, service-level commitments, invoices, maintenance agreements, licenses, warranties, insurance requirements, vendor contact lists, and open-ticket histories. Clarify which agreements run with the property, which are held by the seller, and which depend on an individual employee or contractor account. A vendor relationship is not transferable simply because equipment remains installed.
Review operational procedures, not just technical documents. Ask how after-hours outages are reported, who has keys or access credentials for telecom rooms, how tenants are notified, where spare equipment is kept, and how contractors are escorted. For an acquired portfolio, inconsistent local practices can be as disruptive as inconsistent hardware.
Confirm backup and disaster-recovery capabilities for property-management data and critical configurations. Network-device backups, camera configurations, access-control databases, cloud records, and carrier information should be recoverable. Storm-related outages, utility failures, and physical damage can affect several services at once, so recovery priorities should be written down before a disruption happens.
Key diligence standard: assign a named owner and recovery procedure to every system that affects tenant access, connectivity, safety coordination, or property operations.
Readiness must be proven under realistic conditions. GDS Technology’s podcast episode, Is Your Building Ready for Real Operations?, explains why a technically complete environment can still fail during handoffs, escalation, and recovery. A purchase transition plan should include those same practical tests.
Raisa, a commercial real estate client, described the value of this approach: “John assessed our setup and moved immediately. He knew exactly what needed to be done and handled it quickly and professionally. You get a partner who sees the work before you have to explain it.” Due diligence should give a buyer that level of visibility before risk becomes an emergency.
Takeaway: A portfolio is ready for transition only when its people, vendors, documentation, access, and recovery steps are as clear as its equipment list.
How do buyers turn due diligence findings into a post-acquisition technology plan?
Convert findings into a prioritized transition register with four fields at minimum: risk, business impact, accountable owner, and target date. Categorize work as closing-critical, first 30 days, first 90 days, or planned capital improvement. This keeps a damaged fiber pathway from being treated the same way as a cosmetic documentation cleanup.
Address closing-critical issues first: administrative accounts controlled by the seller, expiring circuits, unsupported firewalls protecting active operations, unknown access-control credentials, missing backups, and conditions that could prevent tenant service. Create a documented transfer plan for all vendor portals, billing accounts, domain records, and emergency contacts.
Then establish portfolio standards without forcing unnecessary replacement. Standardize documentation, monitoring, account access, cybersecurity controls, change procedures, asset labels, and incident escalation. Retain functioning infrastructure where it meets operational and security requirements; schedule replacement where lifecycle, capacity, or risk justifies capital work.
Pay special attention to network-switch lifecycle. Switch failures can interrupt tenant openings, security footage, alarm response, and other time-sensitive building functions. GDS Technology’s switch lifecycle guidance for connected buildings explains why planned replacement is safer than waiting for a building-critical failure.
For physical infrastructure gaps, use a documented plan for structured cabling and low-voltage improvements. Define scope, tenant coordination, building access, testing requirements, as-built documentation, and acceptance criteria. That turns a hidden building constraint into a managed capital decision.
Takeaway: The best due diligence report is a funded, owned transition plan that protects occupancy, tenant experience, and long-term asset value.
Frequently Asked Questions
When should IT due diligence begin in a commercial property acquisition?
IT due diligence should begin during the underwriting and inspection period, before closing conditions and transition budgets are final. Early review exposes carrier-transfer issues, unsupported infrastructure, shared systems, and missing documentation while the buyer still has leverage to request records, negotiate remedies, or reserve capital.
Should tenant networks be included in a landlord’s IT due diligence review?
Yes, but the review should distinguish landlord-owned infrastructure from tenant-owned systems. Buyers should identify shared risers, common network equipment, carrier handoffs, suite pathways, access rules, and any services billed through the property. The goal is to understand operational dependencies without assuming ownership of tenant technology.
What is the biggest hidden IT risk in an acquired building?
A common hidden risk is unclear ownership: equipment, cloud accounts, credentials, circuits, or vendor relationships may be controlled by a seller, former employee, tenant, or contractor. If access cannot transfer promptly, the buyer may inherit a working system without the authority to manage, secure, or restore it.
How often should a commercial real estate portfolio refresh its IT diligence records?
Refresh core diligence records at least annually and whenever a property changes ownership, undergoes major tenant improvements, adds building systems, changes carriers, or experiences a significant incident. Keep diagrams, asset records, contracts, credentials, and recovery procedures current so portfolio decisions rely on evidence rather than assumptions.


